
Zero Trust Security: 7 Smart Steps for Businesses
An employee logs in from the office, opens a business application, and starts working. Everything seems normal. But what if that employee’s password was stolen yesterday? What if the laptop is infected, or the account belongs to someone who left the company last month?
This is why simply trusting a user because they have logged in before is no longer enough.
Zero trust security is an approach to protecting digital systems that requires access to be verified and limited rather than automatically trusted. It considers the user, device, requested resource, and surrounding context before allowing access.
For businesses using cloud applications, remote teams, customer portals, and connected software platforms, this approach can reduce the damage caused by compromised accounts and unauthorized access.
Zero trust is not a single product you install and forget. It is a collection of security principles, technical controls, and ongoing practices that work together.
Here are seven practical steps businesses can take to implement zero trust more effectively.
What Is Zero Trust Security?
Zero trust security follows a simple principle: never grant access solely because a user or device is already inside a trusted network.
Traditional security models often rely heavily on network boundaries. Once someone gains access to the internal network, they may be able to reach more systems than they actually need.
Zero trust takes a different approach. It verifies access requests, limits permissions, and continuously evaluates relevant security signals.
This does not mean every employee must repeatedly enter a password every few minutes. Modern systems can use identity management, multifactor authentication, device checks, and session policies to make access decisions with minimal unnecessary friction.
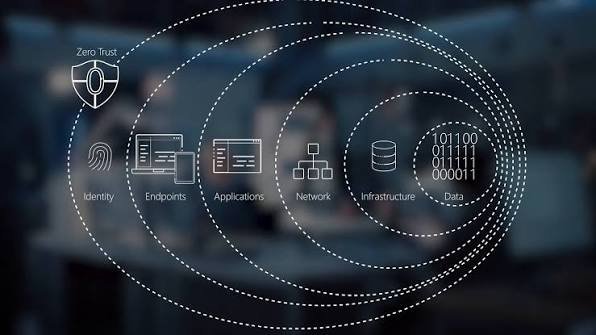
A zero trust strategy commonly includes:
- Strong identity verification
- Least-privilege access
- Device security checks
- Segmentation of systems and networks
- Monitoring and logging
- Secure application access
- Regular review of permissions
The exact implementation depends on the size of the organization, the sensitivity of its data, and the systems it needs to protect.
1. Strengthen Identity Verification
A username and password alone may not provide sufficient protection for important business systems.
Passwords can be stolen through phishing, reused across websites, exposed in data breaches, or shared carelessly. If an attacker obtains valid credentials, the login may appear legitimate unless additional controls are in place.
Start by improving how users prove their identity.
Enable multifactor authentication (MFA). Require an additional verification factor for business accounts, especially administrators, finance teams, and users who can access sensitive information. Phishing-resistant methods, such as security keys or supported passkeys, can provide stronger protection than basic verification codes.
Use centralized identity management. Where practical, manage employee access through a central identity provider rather than creating disconnected accounts for every application.
Review sign-in policies. Apply appropriate controls to unusual sign-ins, risky sessions, and access from unmanaged devices.
Secure administrator accounts. Separate everyday user accounts from privileged accounts and restrict administrative access to authorized personnel.
For example, a staff member signing into a routine application from a managed company laptop may receive a straightforward experience. A suspicious login attempting to access sensitive financial records may require stronger verification or be blocked.
The goal is to verify identity appropriately without making ordinary work unnecessarily difficult.
2. Apply the Principle of Least Privilege
Employees should have the access they need to do their jobs, not automatic access to every system in the company.
This principle is known as least privilege.
Consider a customer support employee who needs to view customer contact details and respond to service requests. That person may not need permission to export the entire customer database, change billing configurations, or manage administrator accounts.
Giving every employee broad access increases the potential damage if an account is compromised or a mistake occurs.
To reduce this risk:
- Assign permissions according to job responsibilities.
- Separate standard user accounts from administrative privileges.
- Limit access to sensitive records and production systems.
- Use temporary, approved access for exceptional tasks.
- Review permissions when employees change roles.
- Remove access promptly when accounts are no longer needed.
Role-based access control can make these decisions easier to manage. More sensitive systems may also require access based on additional attributes, such as device status, location, or the type of information requested.
Do not rely on job titles alone. Two people with similar roles may have different responsibilities and should not automatically receive identical permissions.
Review access periodically and make sure permissions still match actual work requirements.
3. Verify the Security of Devices
A legitimate employee can still create a security risk if their device is compromised, outdated, or poorly configured.
For this reason, zero trust security considers the condition of the device requesting access, not just the identity of the person using it.
Depending on the environment, device checks may include:
- Supported operating system versions
- Current security updates
- Endpoint protection status
- Device encryption
- Screen-lock and authentication settings
- Mobile device management enrollment
- Compliance with company security policies
For example, a business application might allow normal access from a managed laptop that meets security requirements while restricting sensitive downloads from an unknown or noncompliant device.
These rules should be based on risk. Blocking every personal device may be appropriate for some organizations but unnecessarily restrictive for others.
Businesses should also establish a clear process for lost devices, employee departures, and suspected malware infections.
Device verification is particularly important for remote teams because employees may connect from home networks, shared workspaces, and other environments outside the company’s direct control.
4. Segment Networks and Applications
Imagine that an attacker compromises one employee’s computer. If that device can freely communicate with every server and database, the incident may spread much further than necessary.
Network and application segmentation can limit this movement.
Segmentation separates systems into controlled zones and restricts communication between them. Access is allowed only when a connection is required and authorized.
A business might separate:
- Public-facing websites
- Internal business applications
- Production databases
- Development and testing environments
- Administrative systems
- Backup infrastructure
For example, a public website may need to communicate with a particular application service, but it should not automatically have unrestricted access to internal databases or administrative interfaces.
Segmentation can also be implemented through application-level permissions, service identities, cloud network policies, and other controls.
Start with the systems that hold the most sensitive data or present the greatest business risk. Map their dependencies, identify necessary communication paths, and test new restrictions carefully.
Overly aggressive rules can interrupt legitimate workflows, so segmentation should be introduced gradually with monitoring and a rollback plan.
5. Protect APIs and Business Applications
Many modern businesses rely on APIs to connect websites, mobile applications, payment systems, customer databases, and third-party services.
These connections can create security gaps if authentication and authorization are not handled correctly.
An API key or valid login does not automatically mean a request should be allowed to access every available resource.
Apply zero trust principles directly to application design.
Authenticate requests appropriately. Use suitable authentication methods for users, services, and automated processes.
Authorize each action. Check whether the identity can perform the requested operation on the specific resource.
Validate input. Treat data received from clients and external systems as untrusted until it has been checked.
Protect secrets. Store credentials and API keys securely rather than embedding them in source code or public client applications.
Limit exposure. Restrict access to necessary endpoints and apply rate limits where appropriate.
Monitor suspicious activity. Log security-relevant events and investigate unusual request patterns.
For instance, an authenticated customer should be able to view their own order details, not another customer’s records simply by changing an order identifier in a URL.
Developers must enforce these permissions on the server rather than relying only on what the interface displays.
The OWASP API Security Project provides useful guidance on common API security risks and protective practices.
6. Monitor Access and Respond to Suspicious Activity
Zero trust security depends on more than deciding who can enter a system. Businesses also need to understand what happens after access is granted.
Monitoring helps identify unusual activity, investigate incidents, and improve access policies over time.
Useful events to monitor include:
- Repeated failed login attempts
- Unexpected administrator activity
- Access from unfamiliar devices
- Unusual downloads or data exports
- Changes to permissions
- Unexpected API traffic
- Attempts to access restricted resources
Collect relevant logs from identity systems, applications, endpoints, and infrastructure where practical. Protect those logs from unauthorized modification and establish appropriate retention periods.
Alerts should be tied to meaningful risks. A large number of low-value notifications can overwhelm staff and cause genuine incidents to be overlooked.
Create response procedures for common events. If an account appears compromised, the team should know how to revoke sessions, reset credentials, investigate activity, preserve relevant evidence, and restore safe access.
Small businesses without a dedicated security operations team can begin with the alerting and monitoring features already available in their identity provider, cloud platform, and endpoint security tools.
The objective is to detect meaningful problems early and respond consistently.
7. Review Access Continuously
Security permissions often become outdated because businesses change faster than their administrative processes.
An employee moves into another role but keeps their old access. A temporary contractor finishes a project, yet their account remains active. A new application receives broad permissions that nobody reviews afterward.
These are common ways unnecessary access accumulates.
Build regular access reviews into your operations.
At a minimum, review privileged accounts, sensitive data access, third-party integrations, service accounts, and users who no longer need particular systems.
Also establish clear procedures for:
- Employee onboarding and departure
- Role changes and temporary assignments
- Vendor and contractor access
- Expiring temporary permissions
- Reviewing application integrations
- Removing unused accounts and credentials
Automated identity governance tools can help larger organizations manage approvals and periodic reviews. Smaller companies can begin with a documented checklist and a responsible account owner.
Review frequency should reflect risk. Highly privileged accounts may need more frequent attention than access to low-risk tools.
Continuous review does not mean constantly changing permissions without reason. It means making sure access remains justified as people, devices, applications, and business requirements change.
Common Zero Trust Security Mistakes to Avoid
Implementing zero trust can become unnecessarily expensive or frustrating when businesses focus on tools instead of outcomes.
Watch out for these mistakes:
Buying tools before assessing risks: Start by identifying valuable assets, likely threats, and existing access gaps.
Treating MFA as the entire strategy: Strong authentication is important, but it does not replace authorization, segmentation, monitoring, or device security.
Giving every employee excessive permissions: Broad access undermines the purpose of zero trust.
Introducing restrictive policies without testing: Poorly designed access rules can block legitimate work and encourage unsafe workarounds.
Ignoring service accounts and APIs: Automated processes need carefully managed identities and permissions, too.
Failing to define incident procedures: Detection is less useful when nobody knows how to respond.
Trying to change everything at once: A phased rollout helps teams identify problems and learn from early implementations.
The strongest approach is practical, measurable, and proportionate to the organization’s risks.
How to Start Implementing Zero Trust Security
A business does not need to redesign its entire infrastructure overnight.
Start with a small set of high-impact actions:
- Identify critical applications and sensitive information.
- Review who currently has access to those resources.
- Enable strong authentication for important accounts.
- Remove unnecessary permissions and unused accounts.
- Check the security status of devices accessing sensitive systems.
- Restrict communication between systems where broad access is unnecessary.
- Establish monitoring, incident response, and regular access reviews.
Measure progress using indicators such as the percentage of important accounts protected by MFA, the number of unnecessary privileged accounts removed, and the time required to revoke access when an employee leaves.
Expand the approach after the initial controls are working reliably.
For additional guidance, the NIST Zero Trust Architecture publication explains core zero trust concepts and architectural principles.
How HiveRift US Can Help Businesses Strengthen Application Security
Implementing zero trust often involves reviewing application architecture, authentication, permissions, APIs, integrations, and the way business systems handle sensitive information.
Businesses planning a new digital platform or reviewing an existing application can explore the services available through HiveRift US.
Before beginning a security improvement project, document your most important applications, current access controls, sensitive data, external integrations, and known risks. This provides a practical foundation for deciding which improvements should come first.
The objective is not to make every login more complicated. It is to give the right people and systems the right access, for the right reasons, with appropriate safeguards.
Conclusion
Zero trust security helps businesses move beyond the assumption that a user or device should be trusted simply because it has entered a network or logged in successfully.
By strengthening identity verification, limiting permissions, checking device security, segmenting systems, protecting APIs, monitoring activity, and reviewing access regularly, organizations can reduce unnecessary exposure and improve their ability to respond to security incidents.
You do not need to introduce every control at once. Begin with critical accounts and sensitive applications, measure the results, and expand the approach as your security practices mature.
A well-planned zero trust strategy protects business operations while allowing employees to get their work done.
Frequently Asked Questions
1. What is zero trust security?
Zero trust security is an approach that verifies access requests and grants only the permissions required. It does not automatically trust users or devices simply because they are connected to an internal network.
2. Is zero trust security suitable for small businesses?
Yes. Small businesses can begin with multifactor authentication, individual user accounts, least-privilege permissions, secure devices, and regular access reviews before investing in more advanced tools.
3. Does zero trust mean employees must log in repeatedly?
No. Authentication and access policies can be designed to balance security with usability. Session controls, trusted device signals, and risk-based verification can reduce unnecessary interruptions.
4. What is the difference between zero trust and traditional network security?
Traditional models often rely heavily on protecting a network perimeter. Zero trust also evaluates individual access requests and limits permissions within the environment, reducing the assumption that internal access is automatically safe.
5. Does zero trust security require special software?
Not always. Some controls can be implemented using existing identity management, device management, cloud security, and application capabilities. Additional tools may be useful as requirements become more complex.
6. How does zero trust protect business applications?
It helps ensure that users and services are authenticated, authorized for specific actions, and restricted to necessary resources. Monitoring and segmentation can further limit the impact of compromised accounts.
7. How long does zero trust implementation take?
The timeline depends on the number of systems, existing security controls, user requirements, and organizational complexity. A business can introduce foundational controls in stages, while broader enterprise implementations may require a longer roadmap.